Legal and Compliance Review Alongside Technical Review for Security Content
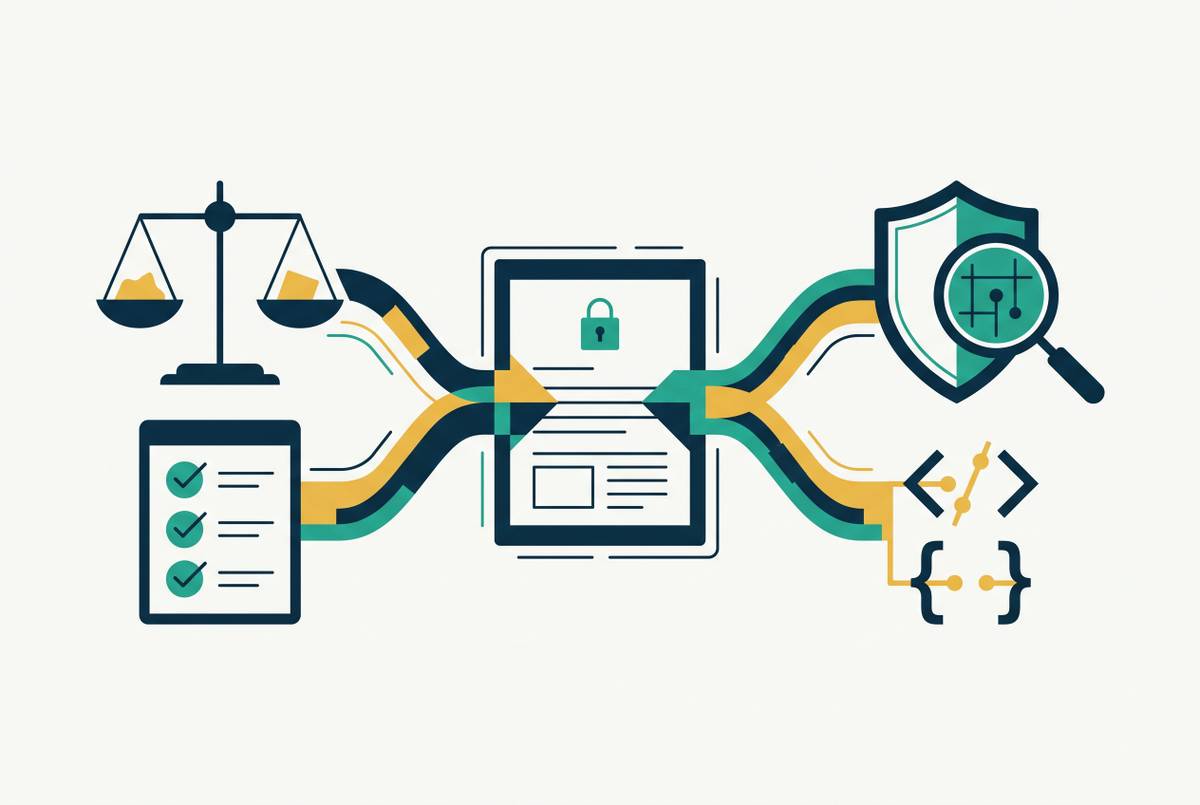
Regulators and buyers now scrutinize the same marketing claims, requiring parallel review.
Top Cybersecurity Marketing Agencies Editors
Vendors must update security content when threats evolve or risk losing credibility.
Regulators and buyers now scrutinize the same marketing claims, requiring parallel review.
Automated checks catch falsifiable facts, but experts must weigh context and evidence quality.
Precise technical claims help both engineers and executives verify security product purchases.
Expert reviewers catch technical gaps that smooth writing cannot hide from security professionals.
Security content needs ongoing updates as threats evolve faster than publication cycles.
Compliance claims need framework-specific review, not just technical accuracy.
Practitioners block deals before demos begin—earn their trust with specificity over marketing.
Format-specific checklists catch the errors each security content type uniquely produces.
Practitioner reviewers catch credibility gaps that editorial teams alone will miss.
Use threat intelligence to decide which security topics actually matter to buyers.
Dynamic threat intelligence, not quarterly planning cycles, should drive security content calendars.