MITRE ATT&CK Framework as a Content Mapping Tool
Map your threat content to real attacker behavior, not a keyword list.
Global security spending hits $244.2 billion in 2026, up 13.3% from the year before. That's a mountain of budget with a vendor logo stapled to every dollar of it, all publishing into the same feed, all fighting for the same fifteen seconds of a security engineer's scroll. Spending keeps climbing. Trust in the content that's supposed to justify it does not, and the two lines on that graph are heading in opposite directions.
The people who actually read this stuff are an engineer, an architect, a SOC lead. Somebody who can smell a keyword-stuffed listicle from three tabs away, because they spent the morning staring at a SIEM and the post in front of them clearly hasn't. Most vendor content still gets built off a content calendar or a keyword list, not off the actual techniques an attacker is running against that reader's stack right now.
Five paragraphs about "the evolving threat landscape," and a practitioner clocks, almost instantly, that nobody who wrote it has looked at an alert queue in years. That mismatch is the security content equivalent of a dentist recommending a toothpaste he's never used. It costs vendors the one audience whose trust actually turns into a signed contract.
MITRE ATT&CK's Grounding in Observed Behavior as the Property That Matters
ATT&CK is a public knowledge base of adversary tactics, techniques, and procedures, maintained by the MITRE Corporation. The structure runs in layers, and the layering is the whole point. Tactics are the adversary's goals: Initial Access, Lateral Movement, and so on. Techniques are the specific methods used to hit those goals. Sub-techniques break a technique down further into its documented variants. Each layer gives a different zoom level, and that matters once you start thinking about content instead of just defense.
The framework covers Enterprise (Windows, Linux, macOS, cloud), Mobile, and ICS/OT. A framework covering one platform would be a decent reference document. One covering all three is closer to a map of the entire battlefield.
The part vendors keep skipping past is that every single entry in ATT&CK ties back to an observed action, cited, with a source. Not theory. Not a kill-chain diagram somebody drew on a whiteboard five years ago and never touched again. That's why practitioners trust the framework itself, and it's exactly the property that content built on top of it can inherit, instead of asking readers to take the vendor's word for it.
How the framework's structure maps onto a content architecture
Enterprise ATT&CK has 15 tactics. Treat each one as a topic cluster, each technique under it as a distinct editorial angle, and each sub-technique as a depth layer for the more advanced pieces. Nobody has to invent a content calendar from scratch here. The taxonomy already exists, so the job is walking the tree, not building one from nothing.
MITRE documents 11 separate use cases for ATT&CK, and each lines up with a content format almost too neatly. Threat intel prioritization turns into threat briefings. Red team exercises turn into adversary emulation reports. Gap assessment turns into maturity and audit content. Control validation turns into proof-of-concept case studies.
The domain split (enterprise, cloud, mobile, ICS) does the same job for audience that tactics do for topic. A cloud security engineer and an OT plant engineer are not reading the same blog post, and handing them one anyway is how vendors end up with a firehose of undifferentiated "cybersecurity content" that nobody in particular asked for.
The technique entries themselves aren't blank pages either. Each one ships with a description, documented examples of threat groups using it, detection strategies, and mitigations. That's most of a draft sitting there already, waiting for a writer instead of a keyword researcher.
Using live threat intelligence to decide which techniques to write about first
Security practitioners don't defend against all 222 techniques with equal urgency, and content shouldn't cover them with equal urgency either. Writing about every technique with the same flat energy is a spreadsheet exercise dressed up as a publishing calendar.
Practitioners instead figure out which threat actors matter to their environment, pull the documented TTPs for those actors, and point limited defensive resources at that specific list. They figure out which threat actors matter to their environment, pull the documented TTPs for those actors, and point limited defensive resources at that specific list. Content should follow the same logic. Prioritizing by actual threat actor activity relevant to a given customer segment is what separates content that earns credibility from content that just claims it on a badge in the footer.
Open-source intelligence tools already map threat actor behavior directly to ATT&CK technique IDs. That builds a clean pipeline: intel comes in, gets tagged with a technique ID, and turns into an editorial angle carrying a citable reference practitioners already recognize and search for.
The Anthropic and Verizon analysis covering March 2025 through March 2026 shows what this looks like at scale. It mapped 13,873 observed actions across 832 banned malicious accounts against the ATT&CK framework, and found the share of medium-to-high-risk, AI-enabled threat actors jumped from 33% to 56% in under a year. That's the bar a technique-mapped threat briefing should clear: specific down to the account count, not vague gestures at "emerging AI threats."
ATT&CK v19's Structural Changes and the Threat Landscape's Direction
The biggest structural change in v19 is a split. Defense Evasion, formerly one giant tactic, is now two: Stealth (TA0005) and Defense Impairment (TA0112). MITRE split it because evasion behavior had outgrown a single bucket, both in size and in how varied the techniques inside it had become. Of the techniques that used to sit under Defense Evasion, 94% got redistributed across the two new tactics.
That's an editorial signal as much as a taxonomic one. Adversary evasion is now big enough to support two separate content tracks: one on hiding behavior (Stealth), one on actively degrading a defender's tools (Defense Impairment). Different audiences, different detection logic, different mitigation advice. Any vendor still mapping content against the old single-tactic version is working off a stale map, and probably doesn't know it yet.
v19 also added techniques tracking AI-enabled and social engineering activity, and two entries deserve a direct look. Campaign C0062 documents GTG-1002, an assessed PRC state-directed cluster, using Claude Code to autonomously run a multi-stage espionage campaign. LAMEHUG (S9035) is the first documented malware to query a large language model during live operations, tied to APT28. Both are specific, citable entries sitting in the ATT&CK database right now, not speculation about what next-generation attacks might someday look like.
v18, the release before it, added Enterprise techniques for Kubernetes, CI/CD pipelines, and cloud databases, plus CTI coverage for software supply chains, cloud identities, and attacks on edge and virtualization systems. Any vendor serving cloud-native or DevSecOps customers should read that list as an open assignment sitting in the backlog, not background trivia to skim past on the way to the next release.
The ATT&CK Navigator as a visual content asset, not just an internal tool
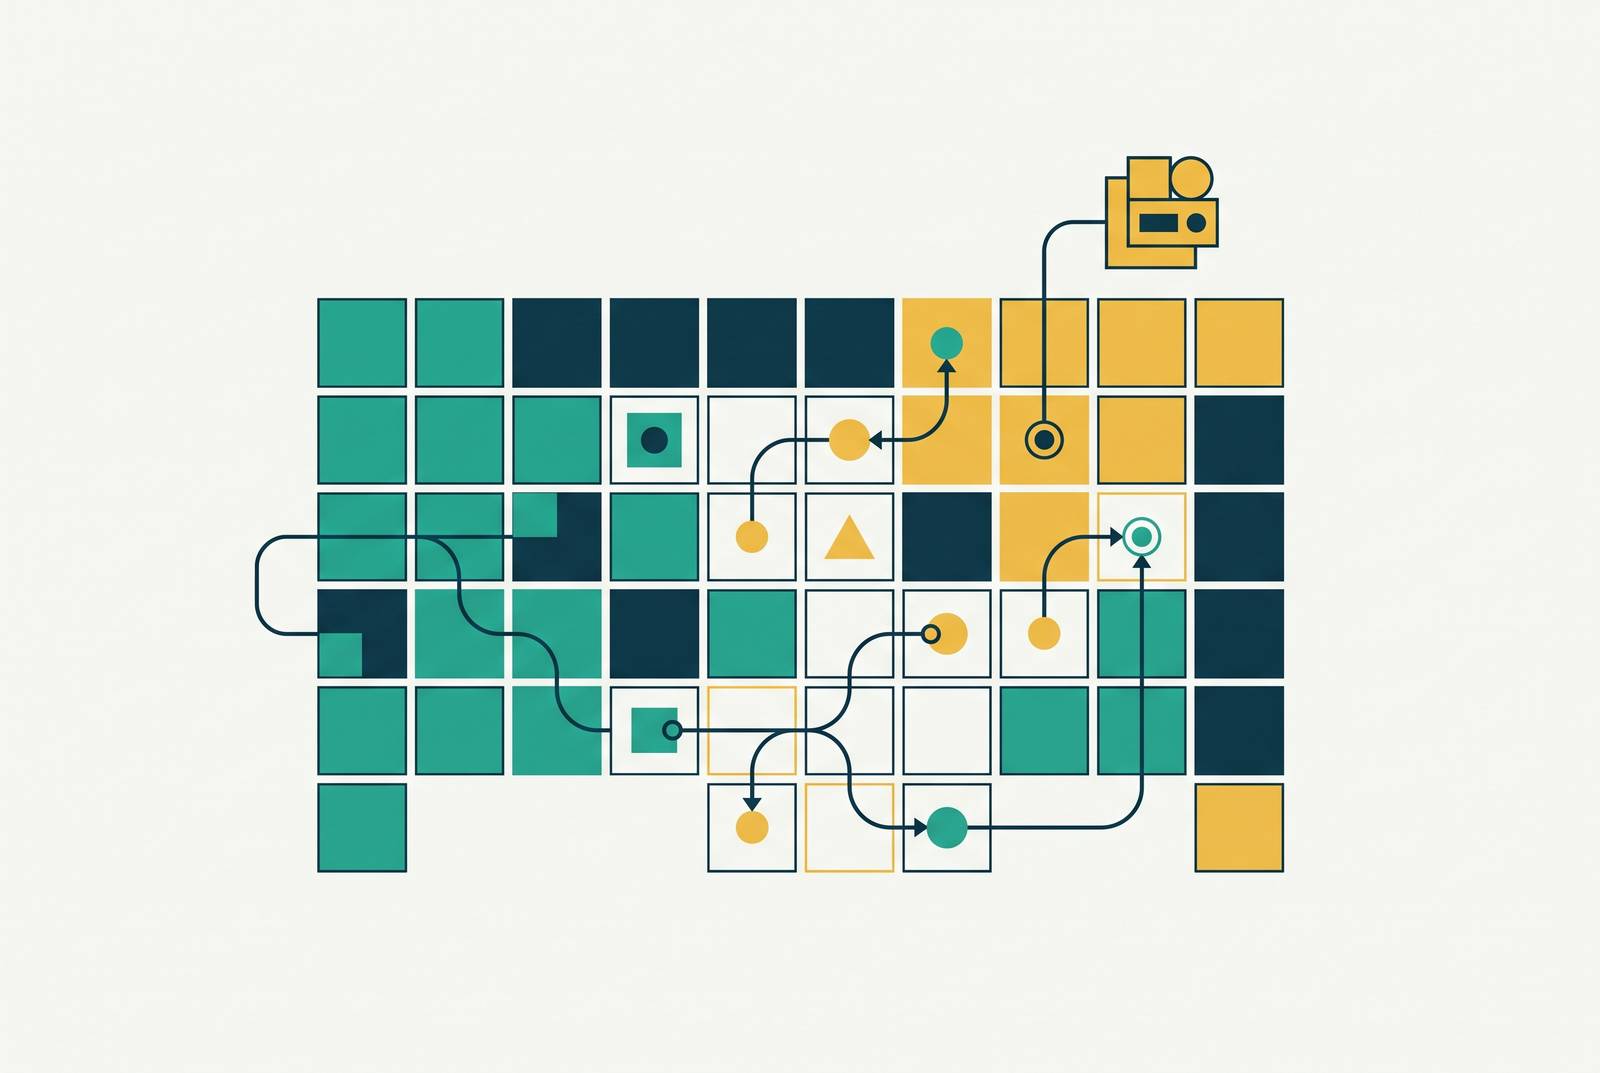
The Navigator turns a security program's technique coverage into a heat map: green for covered, red for gaps. D3FEND has already pulled in more than 128,000 users globally. Neither tool is a niche reference anymore.
Inside most security teams, the Navigator already gets used the same handful of ways: pulling SIEM detection rules mapped to ATT&CK and importing them to check coverage, sharing that coverage map with leadership, overlaying a specific adversary's TTPs for threat intel work, tracking which techniques a purple team exercise has actually tested. The tool is already doing the work. What's missing is the second step, taking that same heat map and publishing it instead of leaving it buried in an internal deck.
Navigator exports as JSON or as a PNG, both of which drop straight into a blog post, a white paper, or a briefing deck with zero extra production work. No design team required, no waiting on a graphics ticket, no back-and-forth over brand colors.
Done right, a coverage heat map anchored to a specific threat group (something like "here's what detection coverage looks like against the techniques APT28 has actually used") does two jobs at once. It's a credibility signal for the practitioner reading closely, and it's a visual an executive understands at a glance without reading a word of the surrounding text.
The ATT&CG Evaluations as the highest-stakes content moment in the vendor calendar
MITRE's ATT&CK Evaluations test enterprise security products against real adversary TTPs pulled straight from the knowledge base, and the results get published publicly. For buyers, that's a rare thing: a comparison point that doesn't run through any vendor's marketing department.
The 2025 Enterprise Evaluations results went public December 10 and 11, 2025, and included the first-ever cloud adversary emulation scenario run as part of the enterprise evaluation. Vendors whose content had already mapped to the cloud techniques added in v18 walked into results day with a head start, ready to explain what the results meant instead of scrambling to catch up overnight.
A vendor that's been publishing technique-level content against the evaluated TTPs all along can contextualize a result with real depth, pointing to specific detections and specific techniques by name. A vendor that hasn't is left writing a reactive press release, and practitioners read those the way anyone reads a statement that opens with "we take this seriously."
Evaluation results are a documentary format: methodology, emulation plan, detection data. That format rewards vendors willing to meet it at the same level of detail. A post walking through what a given emulation scenario actually means for a customer's environment is a different animal than a "proud of our results" post on social media, and readers can tell the difference by the second sentence.
ATT&CK paired with D3FEND: extending the content architecture from offense to defense
MITRE D3FEND (Detection, Denial, and Disruption Framework Empowering Network Defense) is an NSA-funded knowledge graph of defensive countermeasures, mapped directly to the adversary behaviors documented in ATT&CK. It hit 1.0 general availability in January 2025, roughly tripling in size since its initial beta launched in June 2021.
Version 1.3.0 extended D3FEND's coverage into operational technology environments, which completes the pairing across enterprise, cloud, and ICS, the same three domains ATT&CK covers. The logic for content is close to obvious once you see it laid out: ATT&CK answers how attackers operate, D3FEND answers how defenders stop them.
Most vendor content still treats D3FEND as an afterthought footnote, and much of it leaves D3FEND out. That's backwards, because it's a second framework worth mapping content against with the same discipline applied to ATT&CK, since a threat write-up that never gets to the defensive side is only telling the reader half the story. It's a second framework worth mapping content against with the same discipline applied to ATT&CK, because a threat write-up that never gets to the defensive side is only telling the reader half the story, the scary half.
What an ATT&CK-aligned content program looks like in practice
The buying committee now includes more than a CISO reading a vendor blog post over coffee. Start there: identify which threat groups are actually active against a given customer segment, pull their documented TTPs straight from ATT&CK, and build the content backlog from that list instead of from keyword research or a gut feeling about what sounds timely this quarter.
Four filters replace the arbitrary topic-picking most content teams default to. How often relevant threat actors actually use a technique. Whether a recent ATT&CK update (v19 or later) featured it. Whether it showed up in an ATT&CK Evaluations scenario. Whether there's a visible gap in what's already been published.
Every piece of ATT&CK-mapped content has a D3FEND counterpart sitting right next to it, and the strongest programs build in pairs: a threat technique breakdown next to a countermeasure analysis, covering the practitioner's full decision loop instead of just the half where the attacker looks scary. Technique mechanics and detection logic belong in practitioner-grade technical posts. Navigator heat maps and coverage breakdowns belong in leadership-facing visual assets. Threat group profiles work as account-based, sector-specific material. Evaluation result breakdowns serve as mid-funnel proof content for buyers already deep in a purchase decision.
None of this works as a one-time project. ATT&CK updates twice a year, Evaluations results land annually, and threat actor behavior shifts faster than either one. A vendor treating this as a content refresh instead of a standing editorial pipeline will be citing v18 techniques two releases after everyone else stopped caring.