In-House Security Marketing Team vs Agency Outsourcing
Security buyers trust vendors whose marketing reflects genuine technical expertise, not polish.
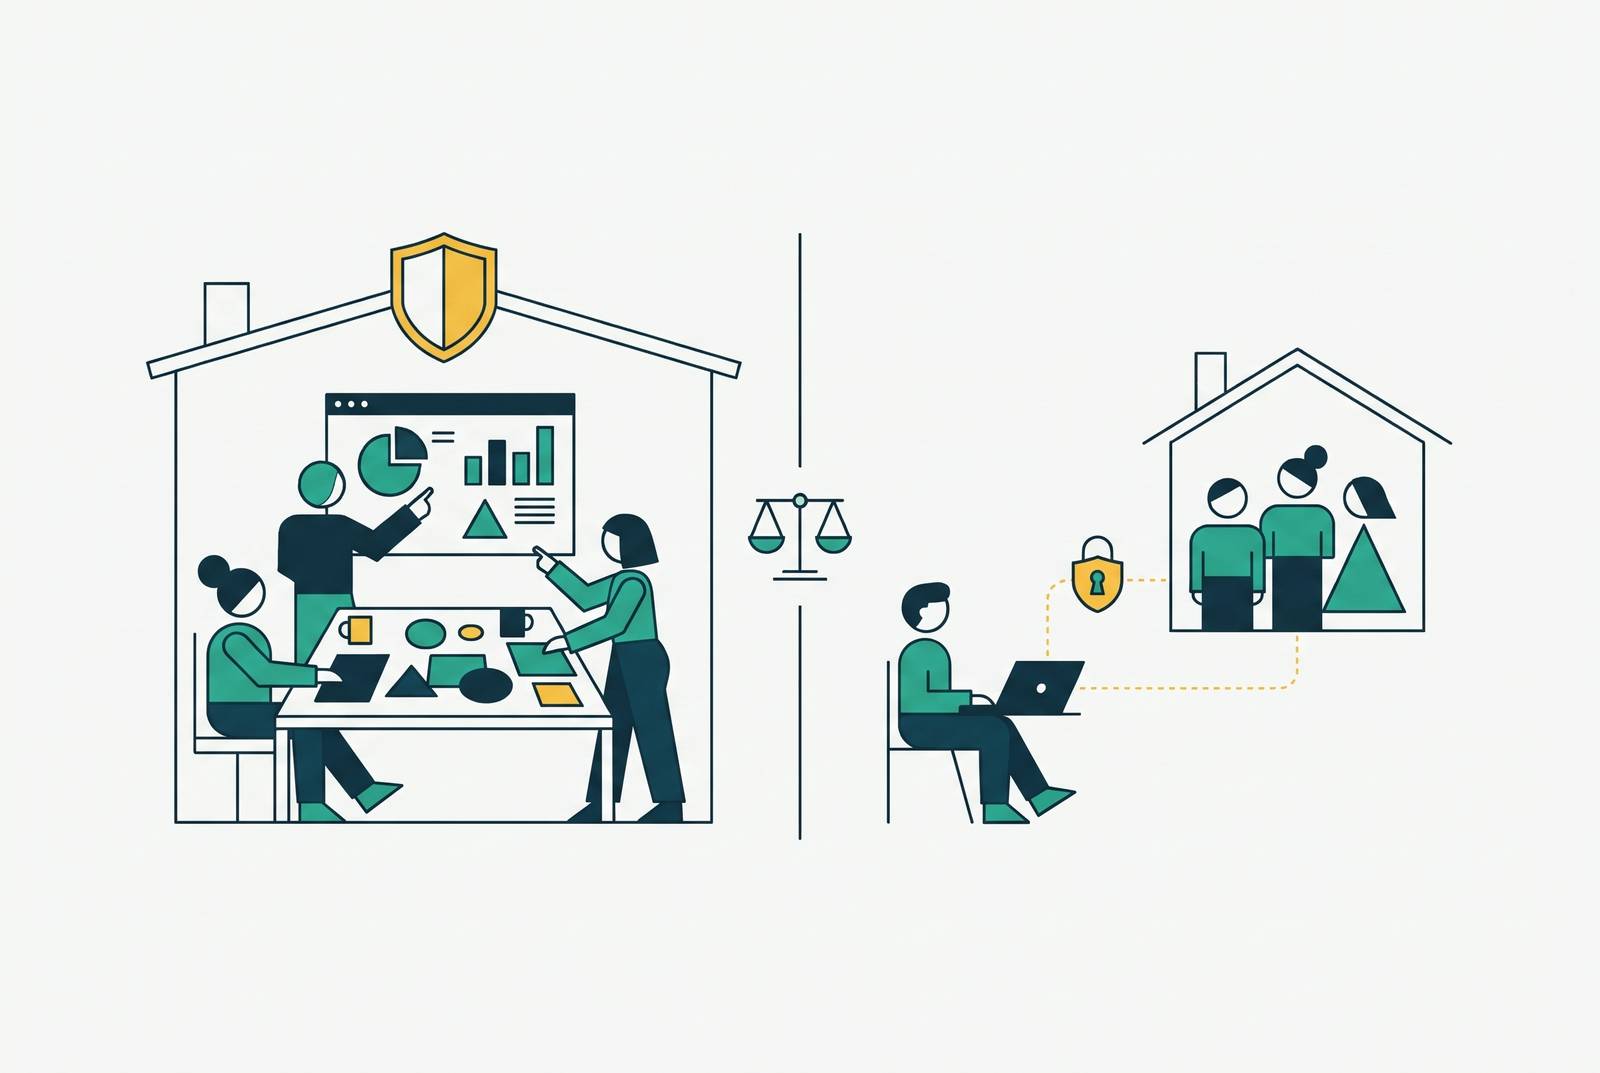
Choosing between an in-house security marketing team and an agency comes down to domain credibility. Security buyers reject content whose technical claims do not hold up. The better model is the one that can earn practitioner trust consistently, with the people, evidence, and resources the vendor actually has.
Why the in-house vs. agency decision is harder in cybersecurity than in any other B2B vertical
Security buyers cannot be bluffed with fluent copy. CISOs, security architects, and security engineers weigh claims against what they have learned over years on the job, often reading whitepapers before they agree to a demo. They recognize when a writer understands the threat landscape and when someone has merely sprinkled acronyms over a sales pitch. The jargon costume rarely survives the first technical question. That makes cybersecurity harder to market than standard B2B, even with more ominous stock photography.
The audience also extends well beyond the CISO. Security engineers want technical depth, those in procurement want total cost of ownership analysis, those in legal want compliance documentation, and those in finance want ROI models. Each group applies its own filter, so a persuasive executive narrative cannot substitute for evidence across the buying committee. Legal and procurement can enter the process early.
Practitioner influence makes that distinction commercially important. Respect earned among technical users can flow upward to the person signing the contract, while campaigns aimed only at the CISO title can leave those influencers cold. Generic AI-generated content adds more noise without resolving that problem. A polished page is now especially weak evidence of expertise. Before weighing payroll against retainers, vendors need to ask whether either can deliver work that readers who know the field take seriously.
What domain credibility actually requires, and why it is difficult to manufacture
Domain credibility is more than familiarity with security terminology. It is the ability to think and write from inside the threat landscape, describing problems in terms practitioners recognize from their work. An accurate account of an attack technique a reader has investigated can establish that connection. A broad claim about stopping sophisticated threats cannot.
A CISO may accept a claim after seeing independent test results, hearing from a peer who deployed the product, or reading technically accurate analysis. Vendor-controlled channels are only part of that judgment. Private Slack groups and peer podcasts also shape what people think, while ISACs mainly help them with threat-intelligence sharing and ISC2 chapters help peers meet and learn from each other. These reflect a market where professional relationships influence trust.
Original threat research, vendor-agnostic implementation guides, and regulatory analysis give practitioners a reason to read even when they have no plans to buy. That makes product claims easier to trust and frees each article from having to wear a sandwich board.
Original research is especially hard to produce whenever it is needed. A new attack technique, honeypot findings, or anonymized SOC incident data can earn backlinks, analyst citations, and authority in sales conversations. Those outputs depend on access to evidence and people who can interpret it. To keep producing them, research, technical judgment, and writing have to work together, and an editorial calendar with empty slots cannot make that happen on its own.
What an in-house team gets right, and where it reliably falls short
An in-house team’s strongest advantage is proximity to the product and the people building it. Product knowledge, internal threat telemetry, and company context accumulate over time instead of requiring a fresh ramp-up with each agency engagement. That knowledge helps writers tell which technical details explain the product and which claims go beyond what it can do. It also makes internal conversations easier to translate into content. The team starts closer to the evidence.
Keeping work inside the company also lowers the risk to operational security. Security vendors handle sensitive infrastructure data, proprietary detection logic, and customer incident details, so confidentiality is more than a contract clause. Working with an outside team offers less protection than keeping analytics and messaging work inside the company. In-house staff can also respond to an emerging threat or urgent sales need without renegotiating scope or waiting for an agency sprint. Speed and discretion can reinforce each other.
The constraint is the breadth of the job. A team covering SEO, content, paid media, marketing operations, and strategy has a substantial fully loaded cost, justified only at a revenue scale many early and growth-stage vendors have not reached. A senior content marketer who has worked in cybersecurity also needs a high annual salary, even before the cost of tools. That person still covers only part of a full-funnel program. One excellent hire is not an entire department.
A generalist learning cybersecurity on the job may produce content that looks appropriate but remains technically shallow. Employment status does not confer domain knowledge, and proximity alone cannot replace it.
What a specialized agency brings, and the real risk of choosing the wrong one
A cybersecurity-specialist agency can supply capabilities an early-stage vendor has not had time to build. Cross-client pattern recognition, established production workflows, and practitioner-calibrated writing can shorten the route to a credible market presence. For a Series A or Series B company without marketing leadership, that can support immediate pipeline needs. The team need not learn the entire category from scratch. Familiarity with threat analysis, compliance requirements, and the practitioner register changes what it can deliver early.
An agency also offers flexibility in execution. A retainer can adjust as go-to-market needs shift, rather than leaving the vendor with the fixed cost of permanent headcount across every discipline. That room to adjust helps when pressure from the board changes spending between quarters. It does not erase the need for internal direction. An outside team can take on work without knowing what the company should stand for.
A generalist agency specializing in name only poses the principal risk: applying a horizontal B2B playbook may produce keyword-stuffed material that practitioners immediately recognize as inauthentic. The vendor’s name appears on the work. Any credibility damage therefore lands with the vendor, regardless of who wrote the draft.
Staff continuity adds another complication. The people pitching an engagement may not be the people executing it six months later, and expertise concentrated in one writer or strategist can leave with that person. Vetting must reach beyond the presentation to produced work, the attack techniques the team has covered in depth, and references from practitioner-level readers.
How CrowdStrike, Mandiant, and Rapid7 built credibility through content, and what the model reveals
Established security brands show that intelligence and research can earn attention independently of a buying cycle. Practitioners use material because it helps with security work. The content serves readers beyond introducing a product.
Practitioners draw on Mandiant’s original threat research in their incident response and detection work. Its authority depends on operational context. Recorded Future illustrates the same mechanism through research used in practitioner workflows. In both cases, the content has value outside a sales conversation. The commercial benefit follows from usefulness.
Peer-sourced narratives give buyers the perspective of people who have used a product, while interactive tools grounded in real risk models let readers engage with evidence. These formats differ from original threat research and require knowledge that a generic content playbook cannot supply.
These examples reveal a content model. Threat telemetry, original research data, peer experience, and sound risk models each back up claims that polished language alone cannot prove. The relevant distinction is whether the publishing process has access to genuine expertise and preserves that expertise in the finished work.
The stage-based logic for choosing a path, and the hybrid model most growth-stage vendors land on
The practical decision begins with the capacity a vendor has today. Early traction and product-market fit can create a need for consistent multichannel execution before marketing leadership is in place. In that situation, a specialist agency can supply established processes and domain-aware people faster than a lone early hire can build the whole function. The recommendation depends on genuine specialization.
An in-house senior hire makes more sense when annual recurring revenue is enough to cover the fully loaded cost and the company needs a steady stream of content. Deep product immersion then has repeated opportunities to pay off. This is different from hiring because a growing company feels it ought to have a marketing department. The workload must justify the commitment. Otherwise, the vendor risks expecting one person to cover strategy, technical content, distribution, and operations equally well.
The hybrid model most Series A and Series B vendors land on divides ownership from execution. An in-house marketer with genuine cybersecurity experience owns messaging, positioning, and brand direction, while external specialists handle work such as SEO, content production, and paid media. That keeps institutional judgment inside the business while extending its production capacity. The external team gains direction without needing unrestricted access to everything the company knows.
Some responsibilities should never be fully outsourced. Messaging and positioning, core brand identity, and important product launches depend too heavily on institutional knowledge for an external team to own them entirely. Where execution capacity already exists but senior direction does not, a fractional senior operator is a legitimate alternative to a full-time CMO-level hire. The choice follows the missing capability.
What to require from any content partner, in-house hire, or agency, to protect practitioner credibility
To protect practitioner trust, vendors should judge potential hires and partners by the work a technical reader will encounter. That means technical accuracy, familiarity with real attack techniques and threat actors, and minimal marketing language. Production quality is useful but insufficient. The evidence of field knowledge has to appear in the reasoning.
For an agency, that standard means reviewing published work for technical depth and asking which threat categories or attack techniques the execution team has covered closely. References from readers who know the technical work test something different from praise by people in marketing. For an in-house hire, direct cybersecurity company experience deserves close attention. A marketer with one to two years inside a security company brings a different background from a generalist whose résumé includes a security client. The distinction is relevant because practitioners judge the resulting content.
The content program itself needs a credible source of substance. First-hand telemetry, observed attack patterns, and original research from the vendor’s environment give writers evidence that cannot be recreated simply by copying a keyword plan. A partner’s process should explain how that evidence becomes publishable work. Editorial scheduling still has a place. It should organize useful material.
Cyberou offers one example as a research and content studio for cybersecurity companies that anchors its programs in live threat intelligence. Its positioning connects content production to the threat landscape and the practitioners who read about it.
That is the standard any arrangement must meet. Whether the writer is an employee, an agency specialist, or part of a hybrid team, the finished work must give a knowledgeable reader a reason to trust the vendor. The contract determines who gets paid. The evidence determines who gets believed.